Why Secure Firmware Alone Won’t Save an Insecure IoT Product
A lot of IoT security conversations still collapse into one narrow question: is the firmware secure?
That question matters, but it is not enough.
In real connected products, compromise does not need to start in firmware. It can begin in weak device identity, exposed cloud APIs, insecure update paths, companion mobile apps, admin dashboards, or backend logic that trusts the wrong thing too easily. If one of those layers breaks, the whole product can still become controllable, observable, or abusable by an attacker.
The common mistake
Security teams often spend serious effort on embedded hardening while leaving adjacent layers less mature:
- weak device authentication or shared credentials
- over-permissive cloud APIs
- insecure mobile or web management flows
- poor authorization between tenants, users, and devices
- update mechanisms that become their own attack path
That creates a dangerous illusion. The device may look hardened while the system around it remains easy to abuse.
The better framing
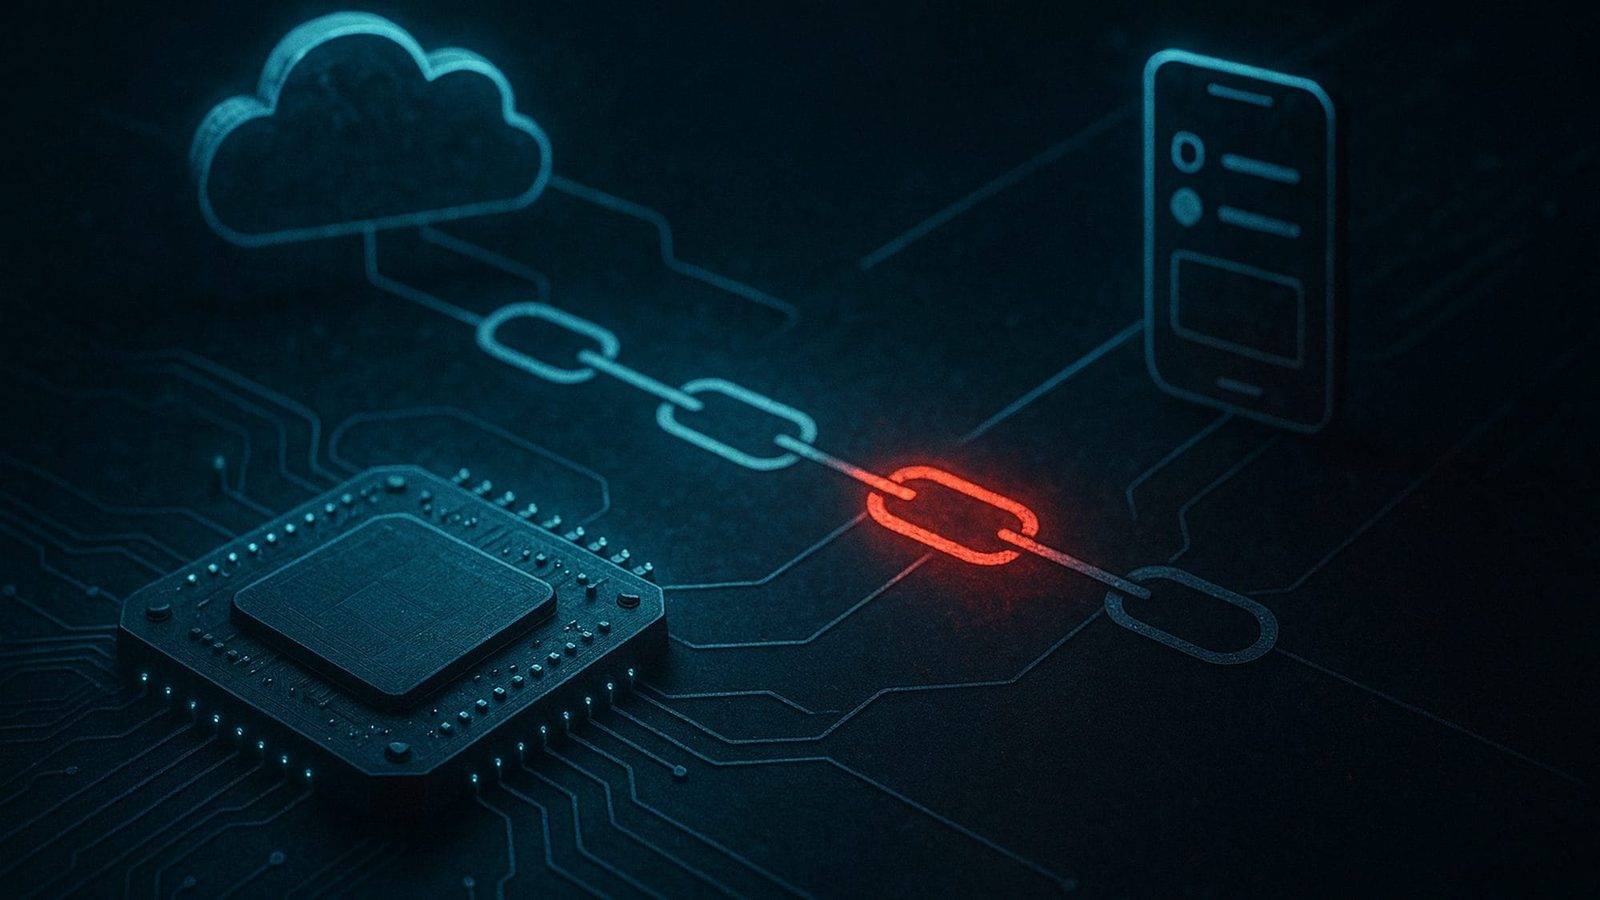
IoT security is not just firmware security. It is trust-chain security.
A secure product has to answer all of these questions well:
- How does the device prove identity?
- What can the cloud trust from the device?
- What can the app trust from the cloud?
- Who is allowed to trigger sensitive actions?
- What happens if one component is spoofed, replayed, or over-privileged?
If those questions are weak, secure firmware alone will not rescue the product.
What stronger IoT defense looks like
1) Harden device identity
Per-device identity, strong authentication, and clean provisioning matter more than many teams realize.
2) Treat cloud APIs like critical attack surface
Your cloud control plane can be just as dangerous as the device itself.
3) Audit companion apps and dashboards
Mobile and web surfaces often expose sensitive workflows attackers can chain into bigger control.
4) Secure the update path
If firmware updates are insecure, the fix channel becomes the attack channel.
5) Review the product as a system
The real risk is often in the connection points between embedded code, cloud logic, and user-facing software.
Why this matters commercially
IoT products are now software businesses with hardware attached. That means a security failure is rarely just a device bug. It becomes a product trust problem, a customer risk problem, and eventually a brand damage problem.
The teams that win will be the ones that stop thinking in isolated layers and start defending the full product trust chain.
If you want more practical breakdowns on AI, IoT, and offensive-minded security design, start here with the LufSec course library.
Reference: Securing Cloud-Based Internet of Things: Challenges and Mitigations
Also, subscribe for new breakdowns on LufSec on YouTube.